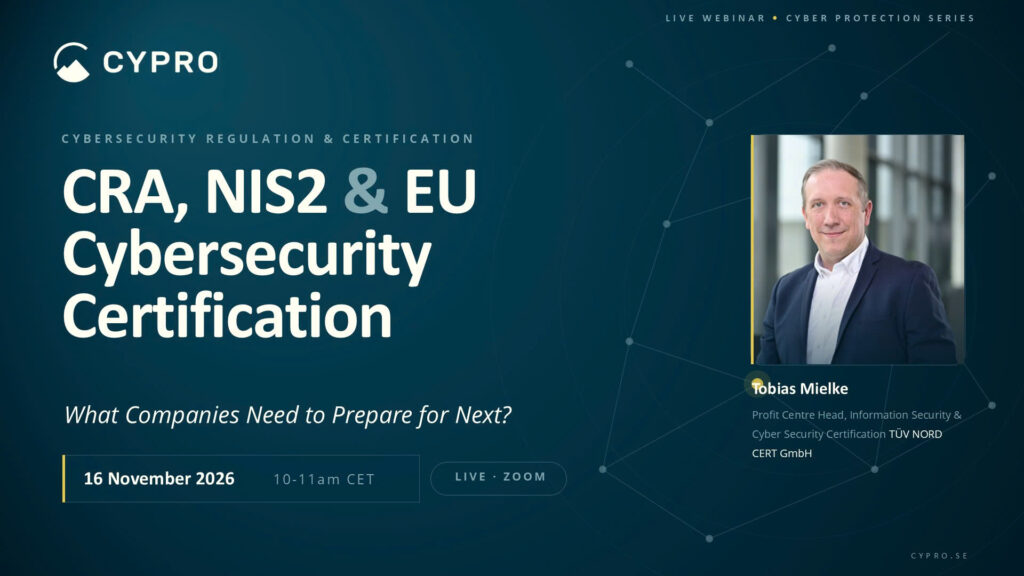
CRA, NIS2 & EU Cybersecurity Certification
About this Webinar
Europe’s cybersecurity regulatory landscape is changing. With NIS2, the Cyber Resilience Act (CRA), the Critical Entities Resilience Directive (CER) and evolving EU certification frameworks, organisations face increasing requirements for security, accountability and resilience.
But what do these regulations mean in practice, and where should companies start?
In this webinar, Cypro welcomes Tobias Mielke from TÜV NORD CERT GmbH to explore the regulatory developments shaping European cybersecurity and the practical steps organisations should consider as they prepare for 2027.
Agenda
- EU cybersecurity landscape: NIS2, CER, CRA and Cybersecurity Act
- NIS2 & CER: Scope, obligations and national implementation
- CRA: Timeline, product classes and conformity assessment modules
- Certification: EUCC, EUCS/C5, ISO/IEC 27001 and more
- Key takeaways and live Q&A
####
Meet the Speaker
Tobias Mielke
Profit Centre Head for Information Security & Cyber Security Certification at TÜV NORD CERT GmbH
An experienced technical expert and auditor, he specialises in cybersecurity certification, international security standards and EU regulatory requirements.